Modern vulnerability management

Turn vulnerability noise into clear action.

CVE Dash brings product-focused vulnerability monitoring, prioritisation, acknowledgement workflows, remediation insight and reporting together in one clean multi-tenant platform.

Multi-tenantSeparate customers, users and settings
Product-firstOnly CVEs relevant to your estate
ActionableResolve, track and report findings
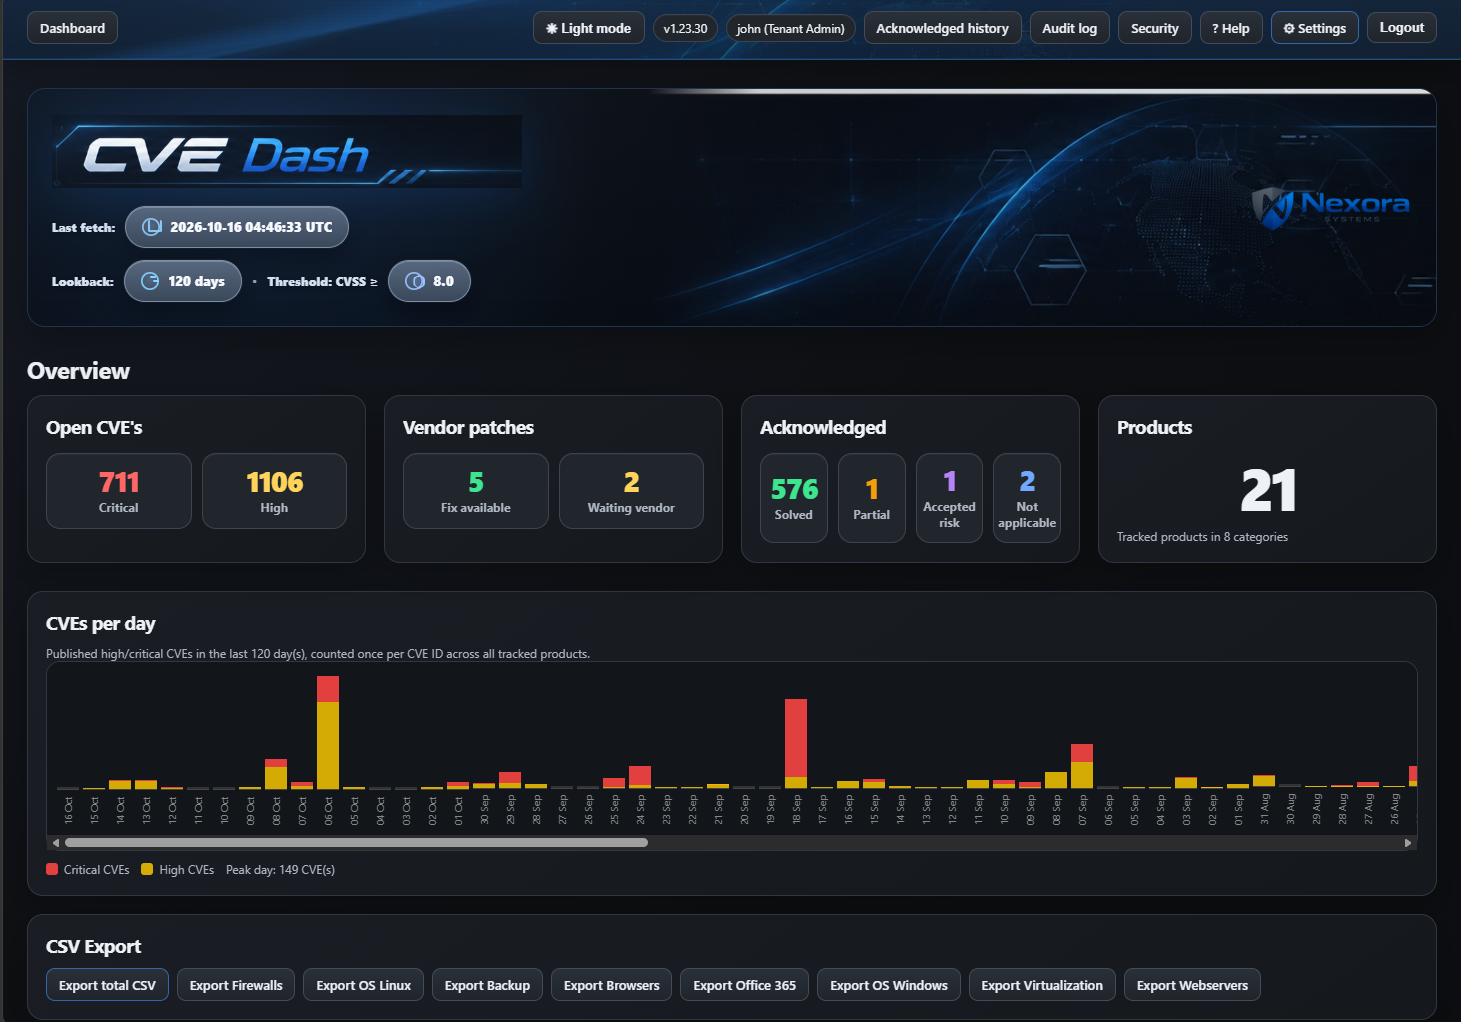
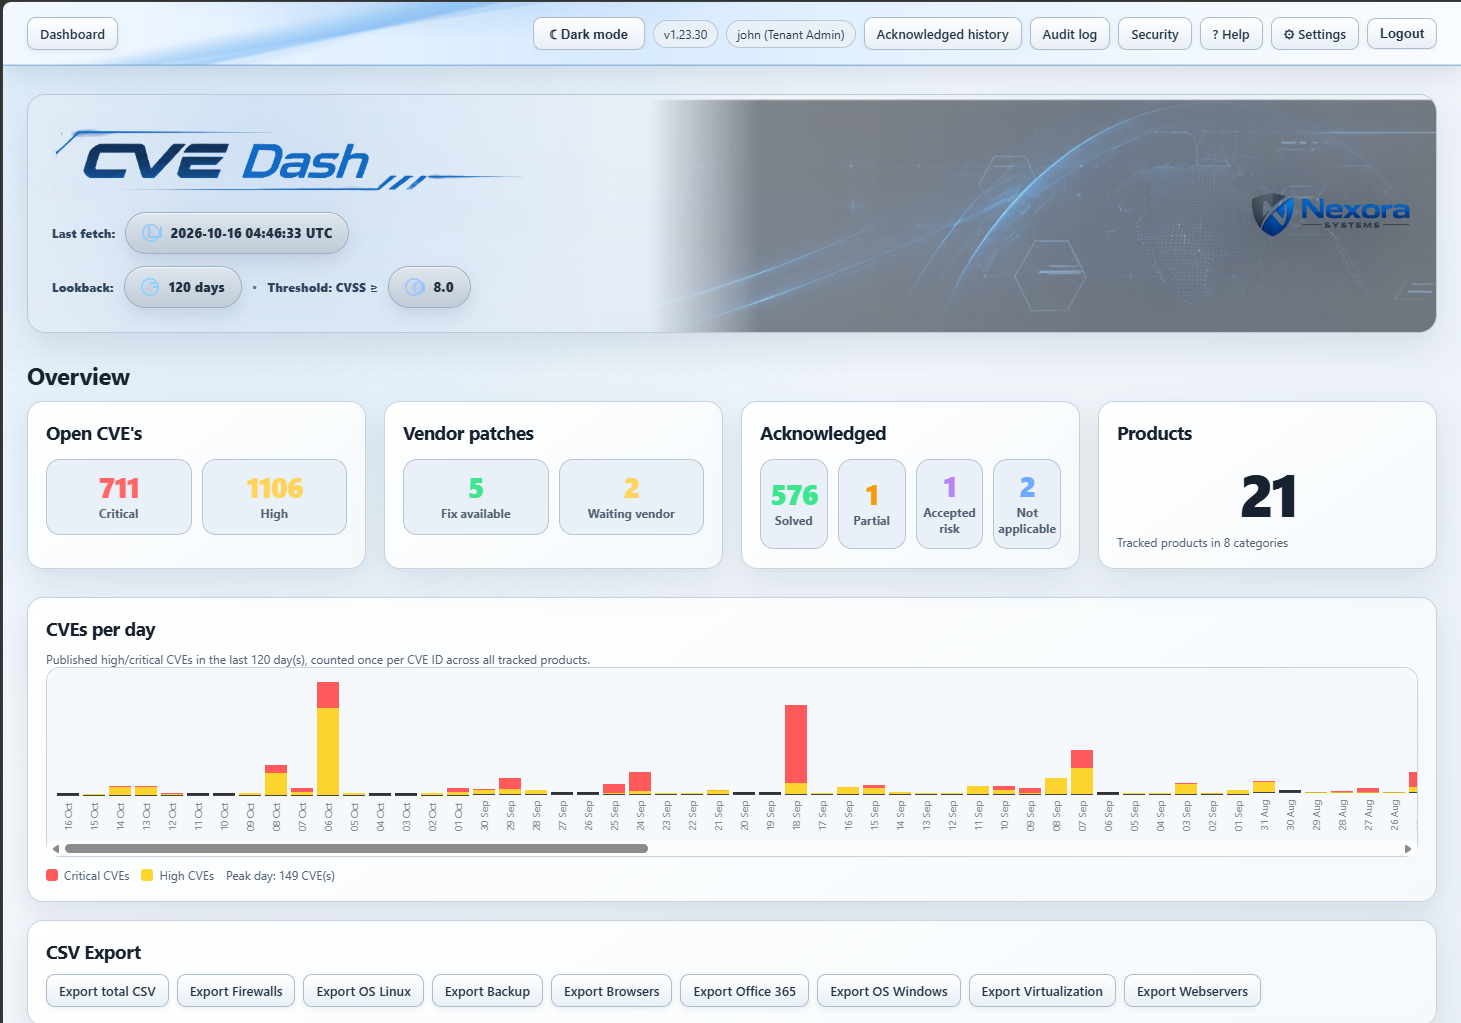
CVE Dash dashboard in dark mode CVE Dash dashboard in light mode
Dark mode dashboard
Click image to enlarge
Core capabilities

Everything needed to keep vulnerability work visible and manageable.

From source ingestion and product matching to operational resolution and stakeholder reporting, CVE Dash keeps the workflow in one place.

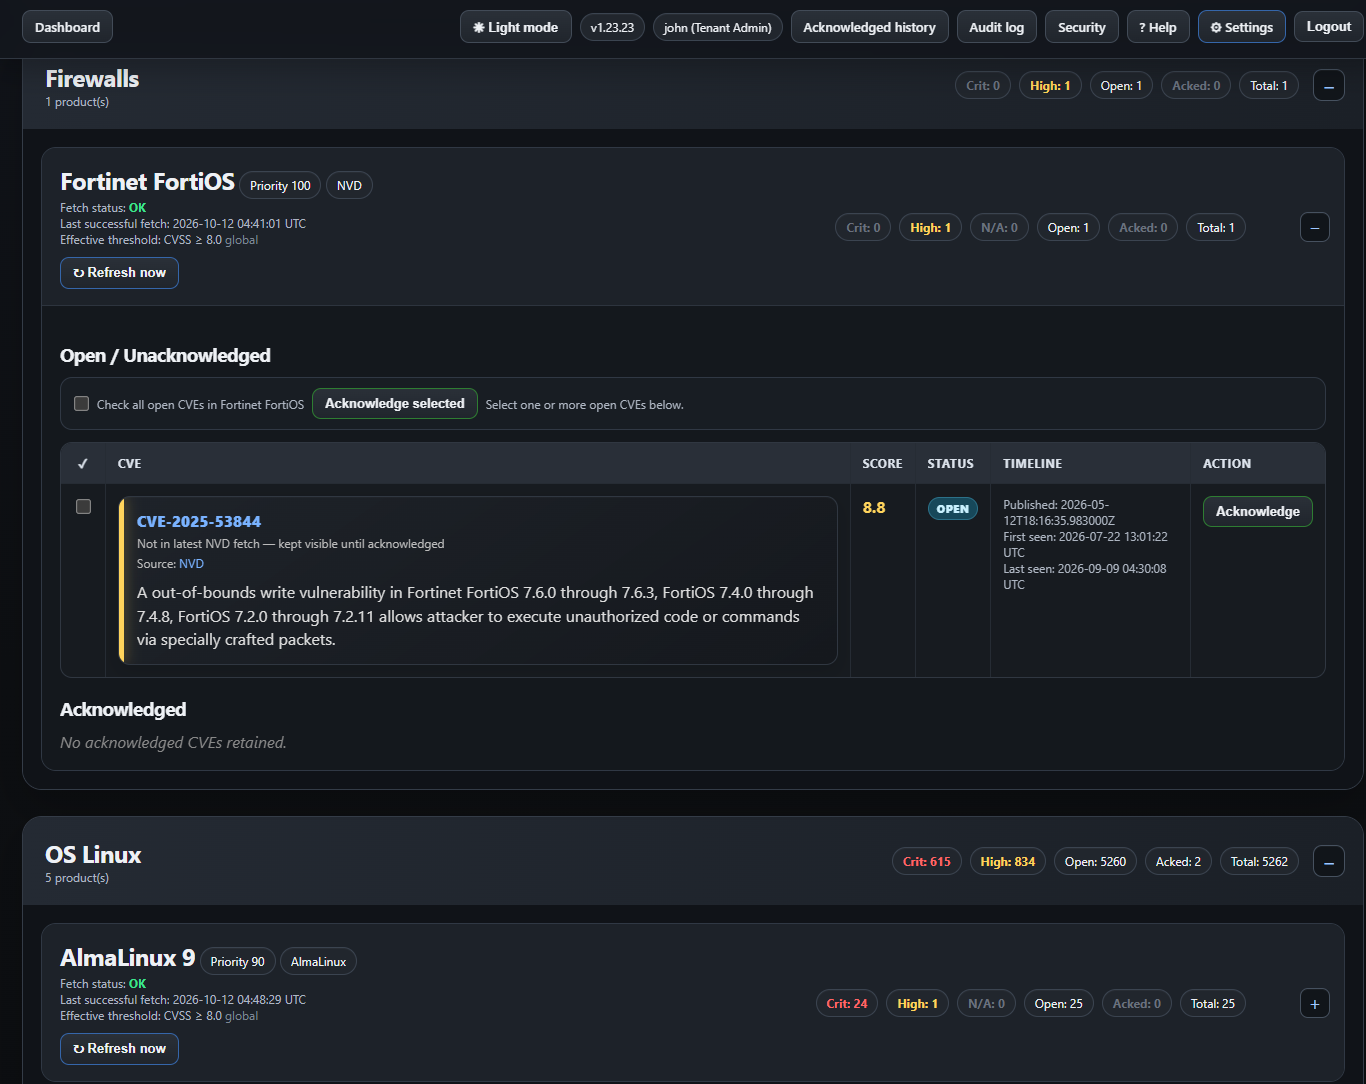
Grouped product dashboard with refresh, acknowledgement and severity totals
Grouped products, per-product counts and operational CVE cards.
Focused dashboard

See what matters by product and severity

Products are grouped into manageable categories with clear critical, high, open and acknowledged counts. Detailed CVE cards put context, score, status and timeline directly in view.

Per-product CVSS thresholds and priorities
Chronological open CVE views
One-click refresh and acknowledgement
Category-level totals for faster triage
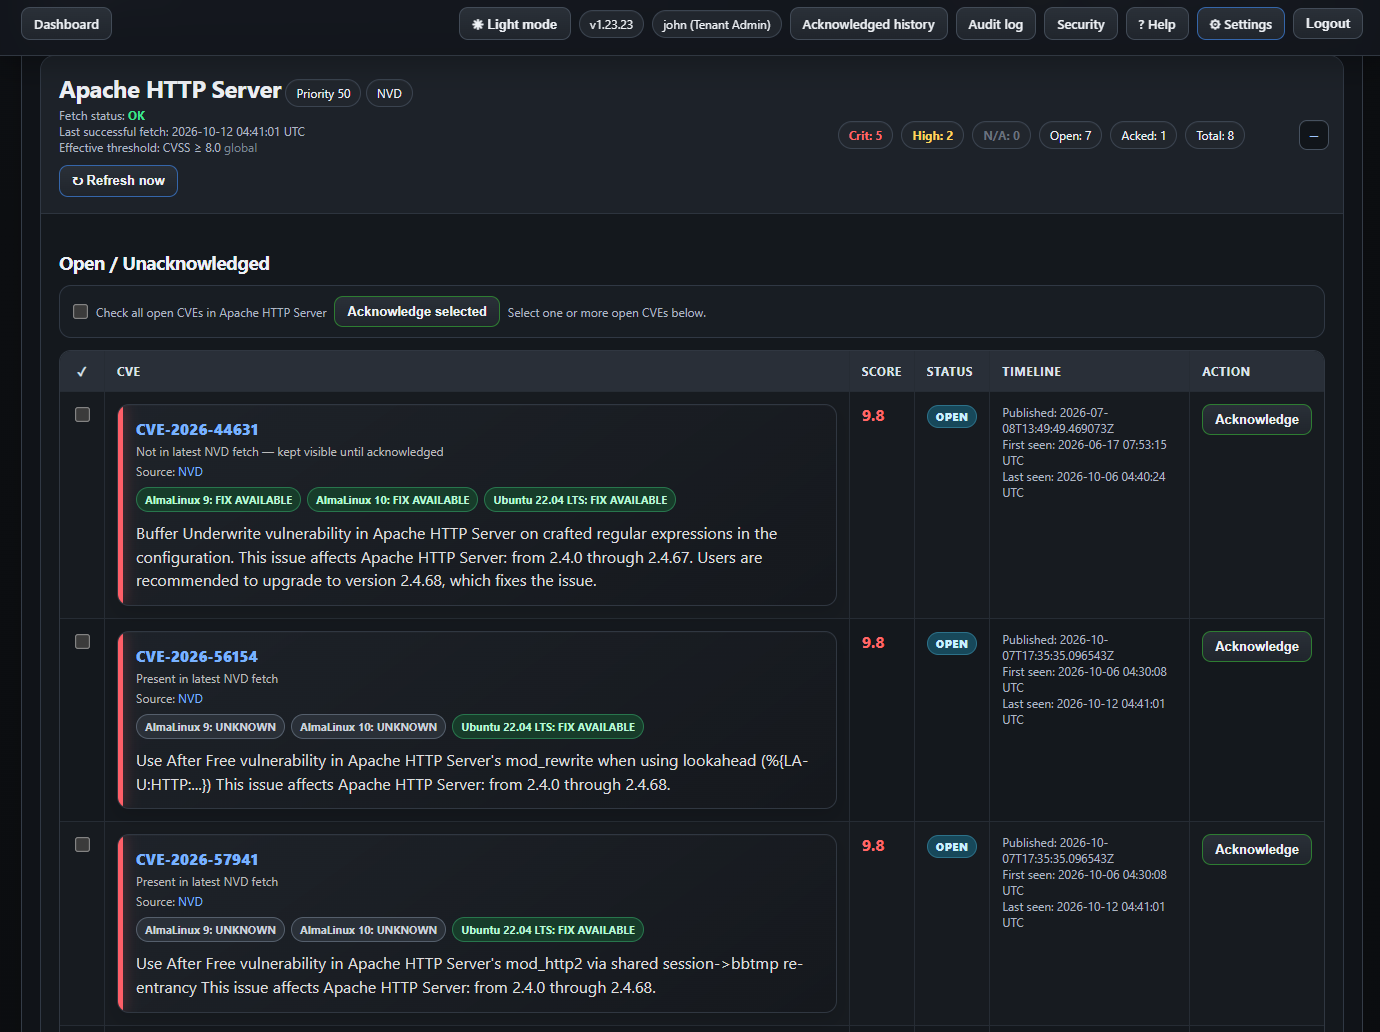
Vendor patch availability shown on CVE cards
Distribution-aware patch availability directly inside each CVE card.
Remediation intelligence

Know when the vendor already has a fix

CVE Dash can enrich matching CVEs with vendor patch availability for the operating systems where a product is actually deployed. Configure platform and package mappings once, then see remediation status directly on each CVE card.

Per-platform FIX AVAILABLE, WAITING VENDOR, NOT AFFECTED and UNKNOWN states
Distribution-aware package mapping such as httpd vs apache2
Vendor advisory and fixed-version context where available
Clear visibility without false compliance claims
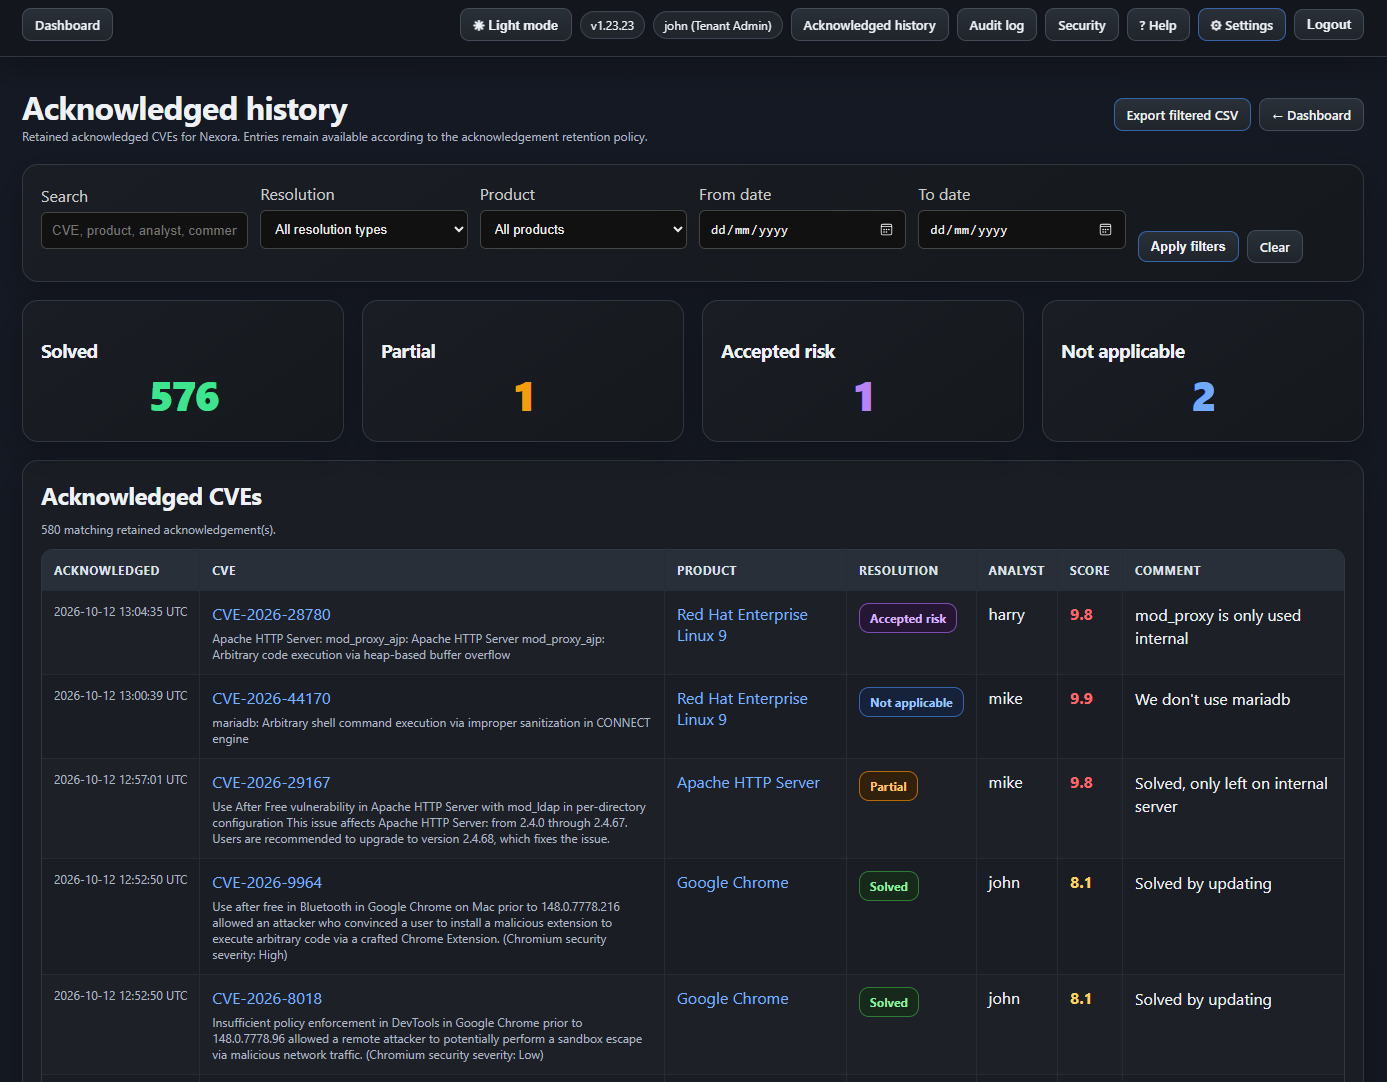
Acknowledgement history table with resolution states
Searchable resolution history with comments, scores and analyst attribution.
Resolution workflow

Track decisions, not just detections

Record whether a CVE is solved, partially remediated, accepted as a risk, or not applicable. Every decision retains analyst, timestamp, comment and score for a defensible history.

Consistent resolution states
Searchable acknowledgement history
Tenant-scoped audit trail
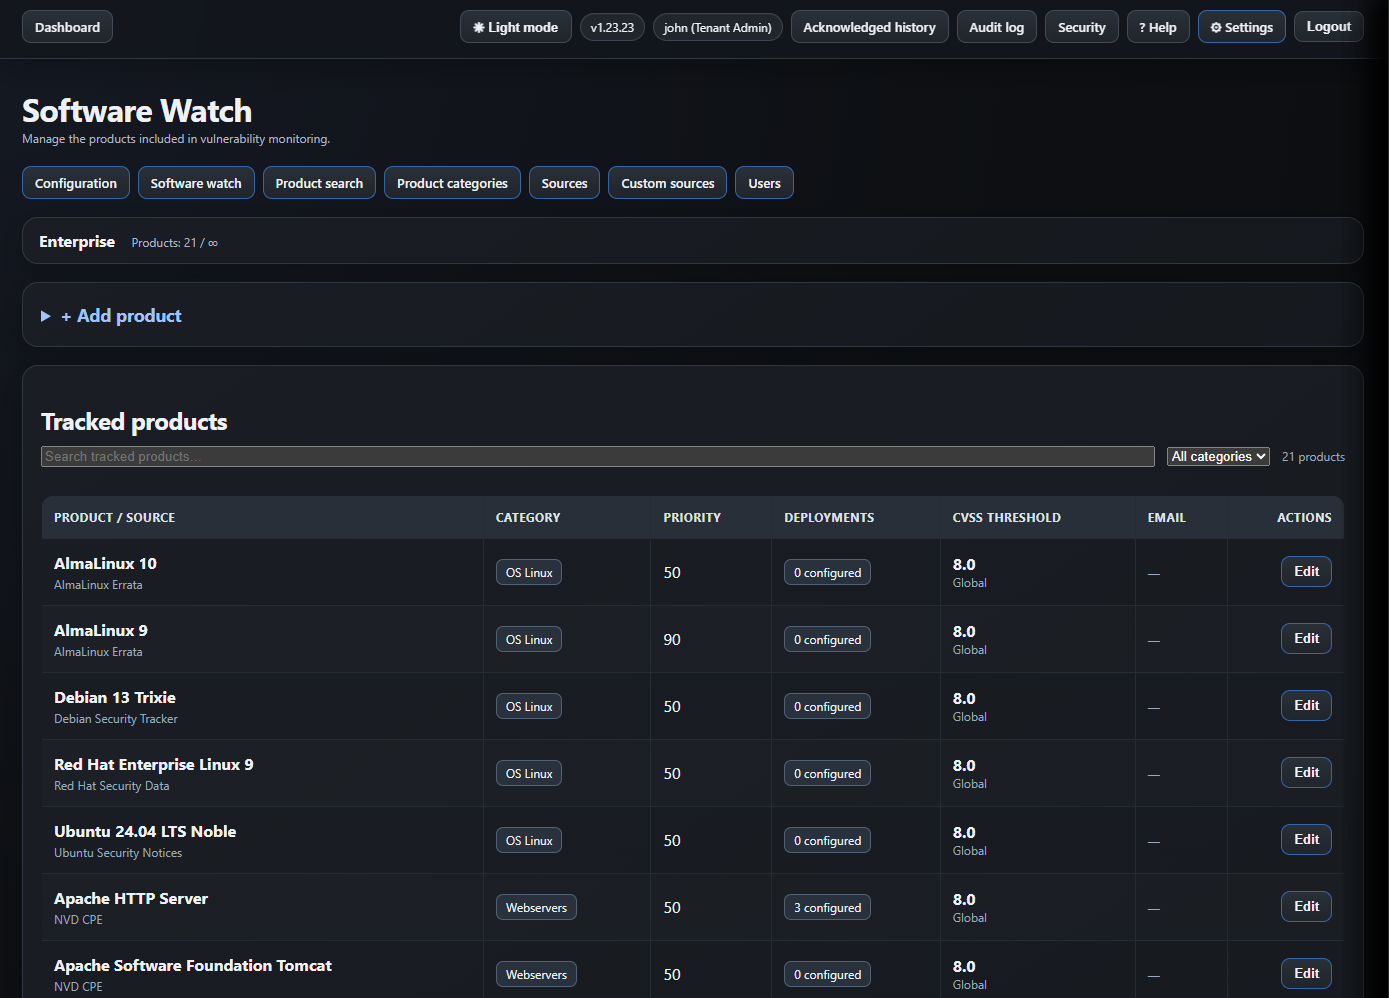
Software Watch tracked products overview
Compact tracked products overview with category filtering.
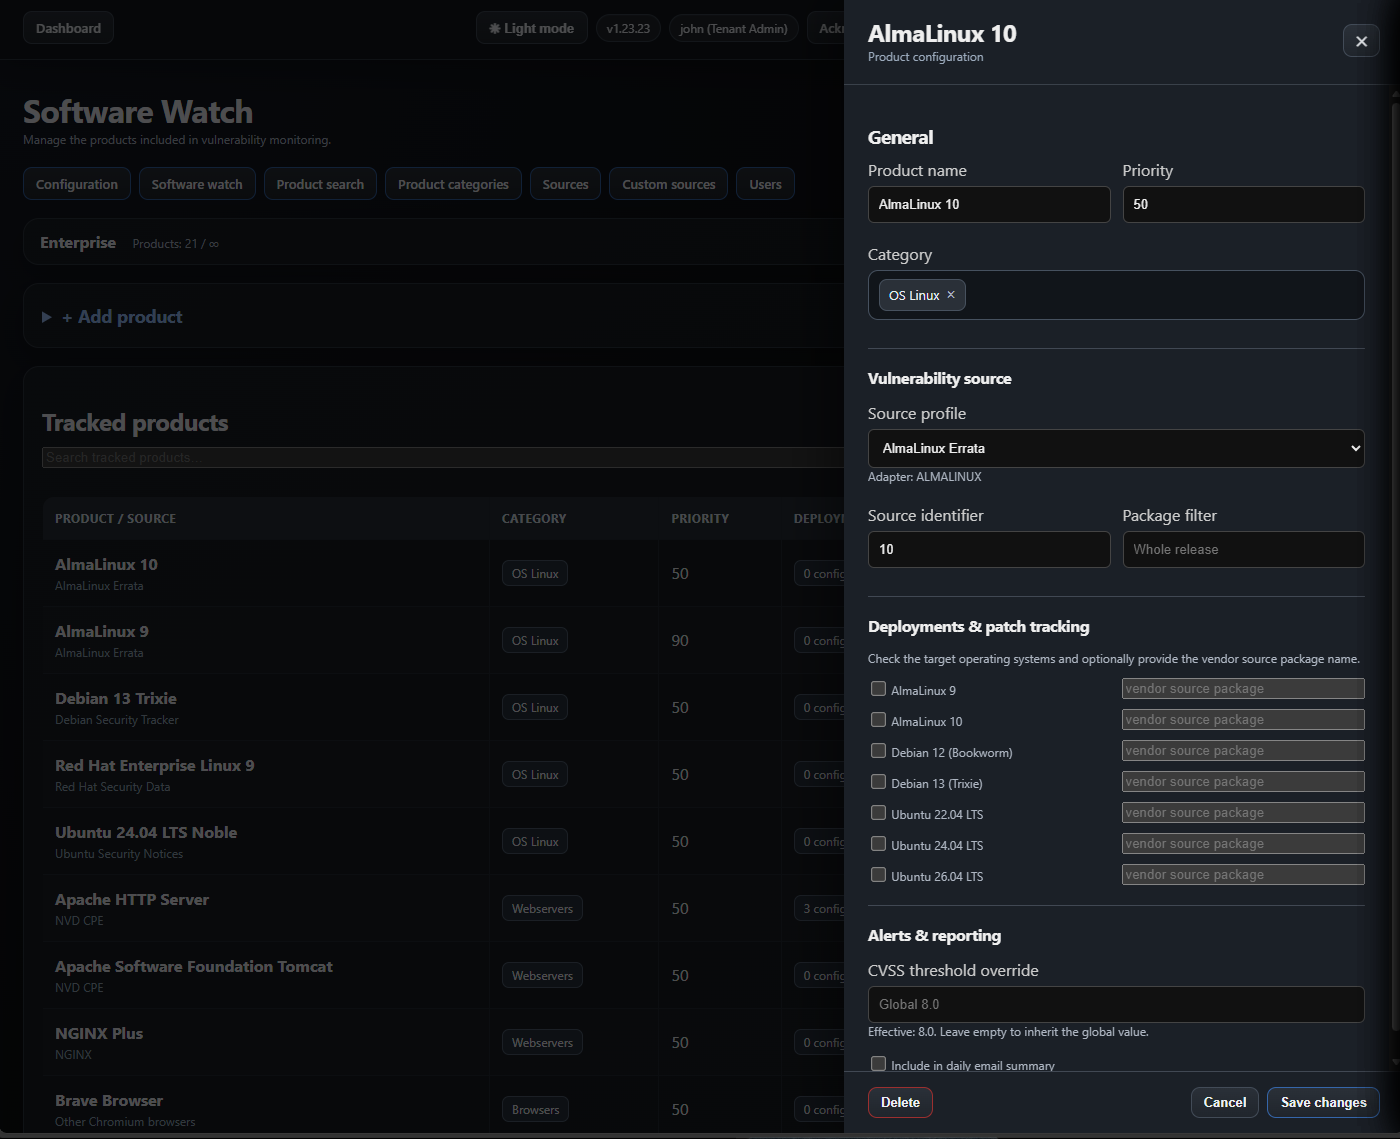
Slide-out product configuration editor
Slide-out editor for source, deployment and alert settings.
Software watch

Configure products without clutter

The tracked products interface keeps the overview compact while moving all detailed settings into a clean side panel. That makes it easy to manage categories, priorities, source profiles, package filters and deployment mappings at scale.

Search and filter tracked products instantly
Slide-out editor for focused changes
Deployment and patch tracking on the same screen
Clear global-versus-override CVSS threshold visibility
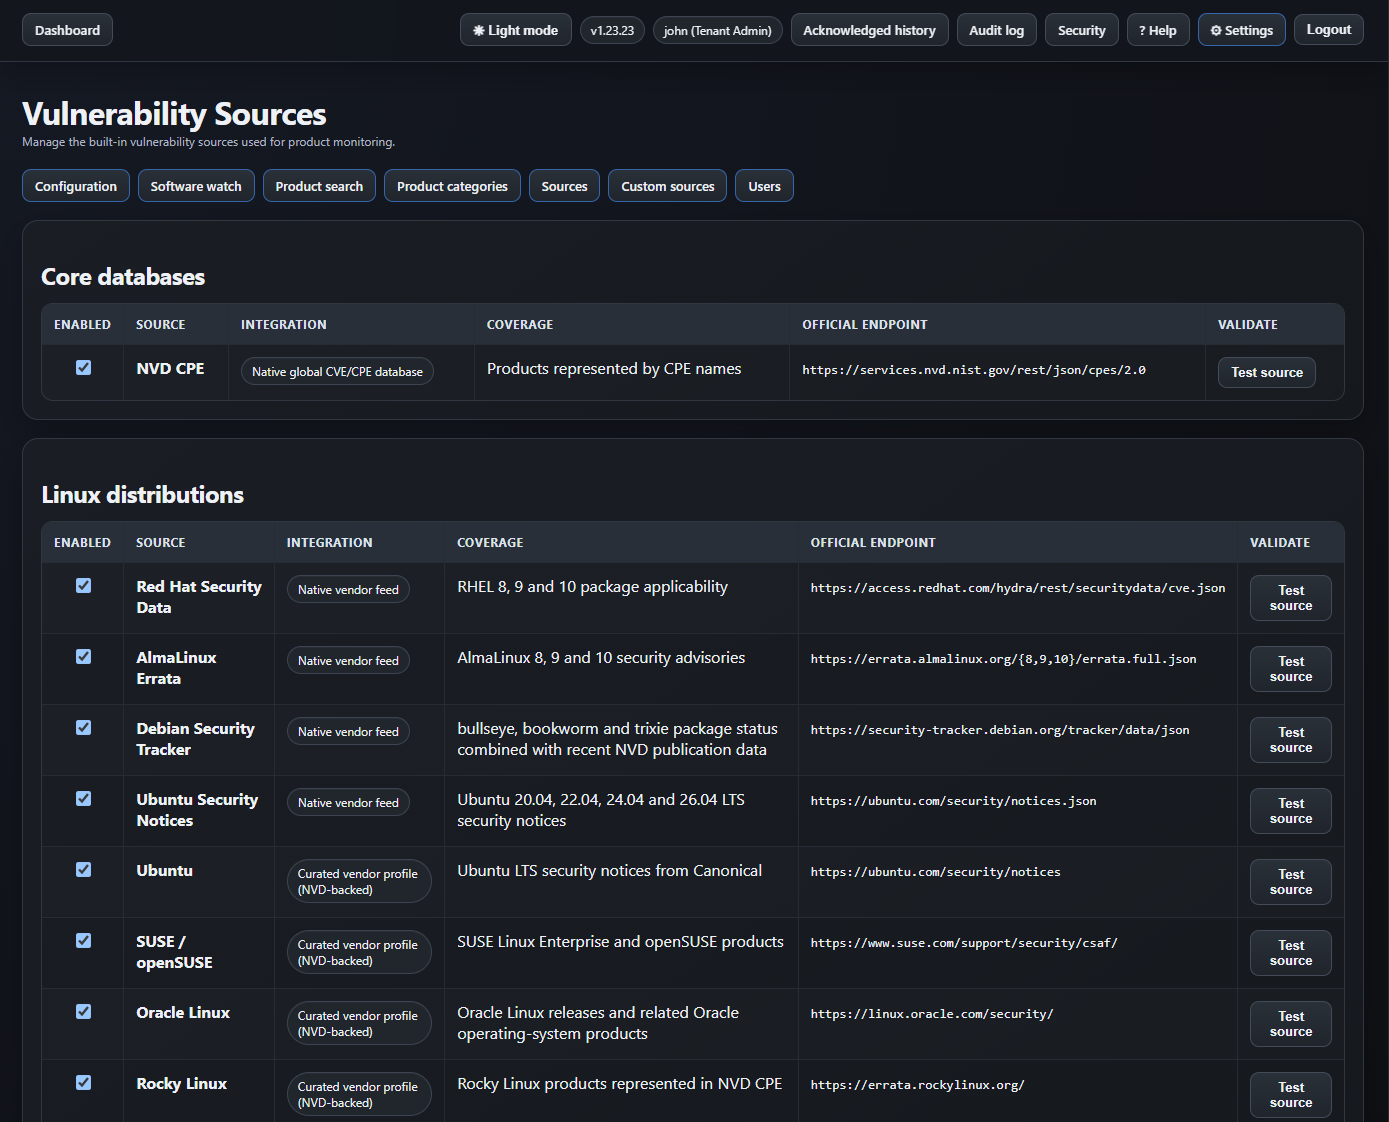
Built-in vulnerability source integrations
Built-in vulnerability source coverage and validation.
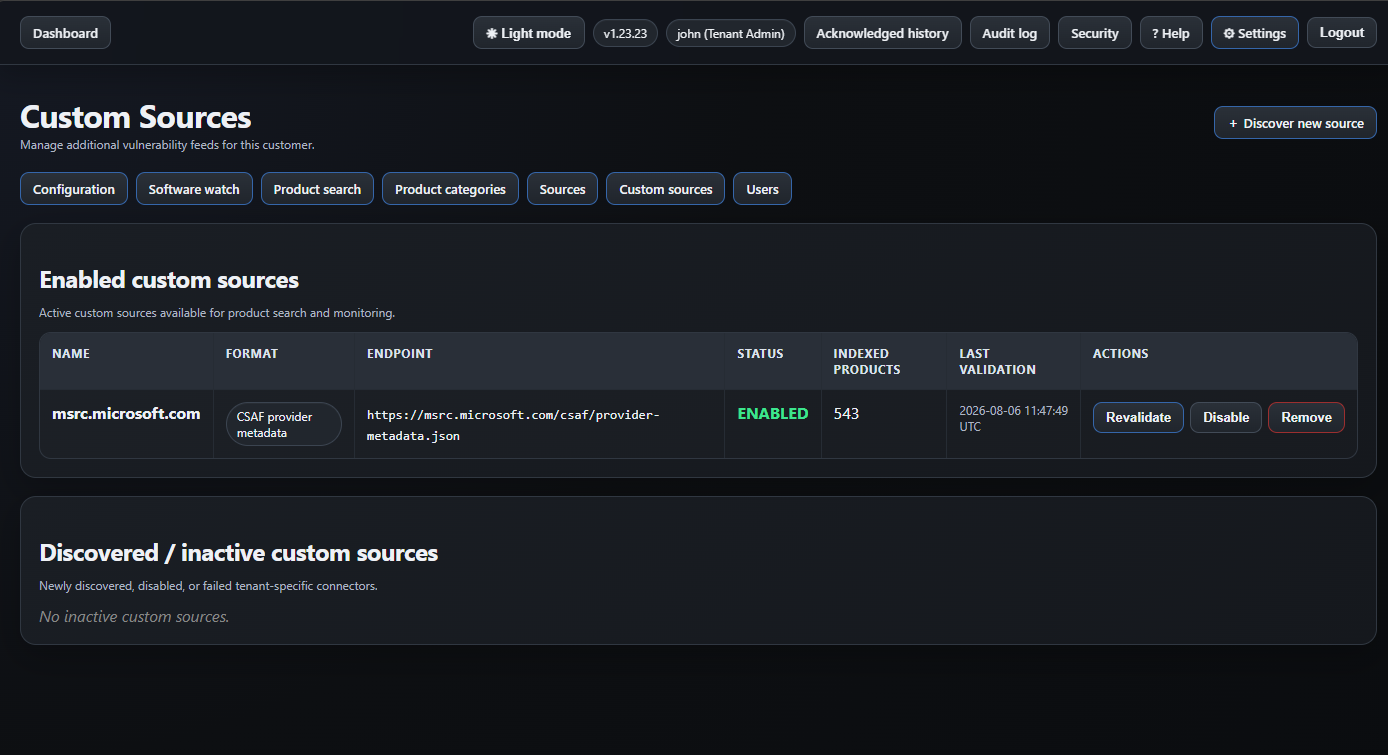
Customer custom sources
Custom source discovery and tenant-specific connectors.
Source intelligence

Combine curated and custom vulnerability sources

Use built-in vendor profiles backed by NVD and specialist feeds, then extend coverage with discoverable CSAF providers and tenant-specific custom sources.

NVD, vendor and CSAF integrations
Source validation and product indexing
Custom source discovery and enable/disable control
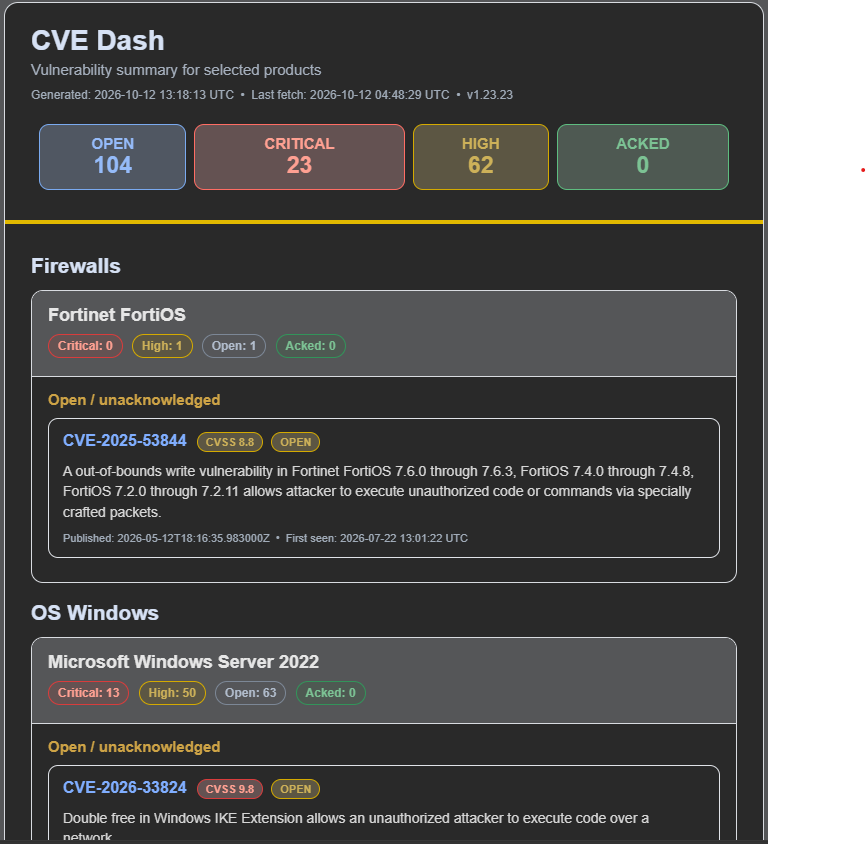
HTML email vulnerability summary
HTML email summaries for stakeholders who do not live in the dashboard.
Reporting

Keep teams informed without dashboard fatigue

Deliver structured email summaries containing the current open, critical, high and acknowledged posture, organised around the products and categories people actually own.

Daily HTML summaries
CSV export by category or full estate
Clear customer-facing presentation
Platform tour

A clean interface for daily vulnerability operations.

Click any screenshot to enlarge it.

Vulnerability management without the clutter.

Sign in to your tenant and turn the latest CVE data into a clear operational workflow.